One customer record
Onboarding, risk score, monitoring and cases share one data model, so nothing lives in a separate system.
Reviews on a schedule
Set ongoing due diligence intervals per risk level and let Bits refresh data and open reviews when they are due.
A complete audit trail
Every rule change, decision and data update is logged with who made it and when.
Four requirements that touch every compliance team, each covered by the same platform.
AML risk score
A documented risk-based approach
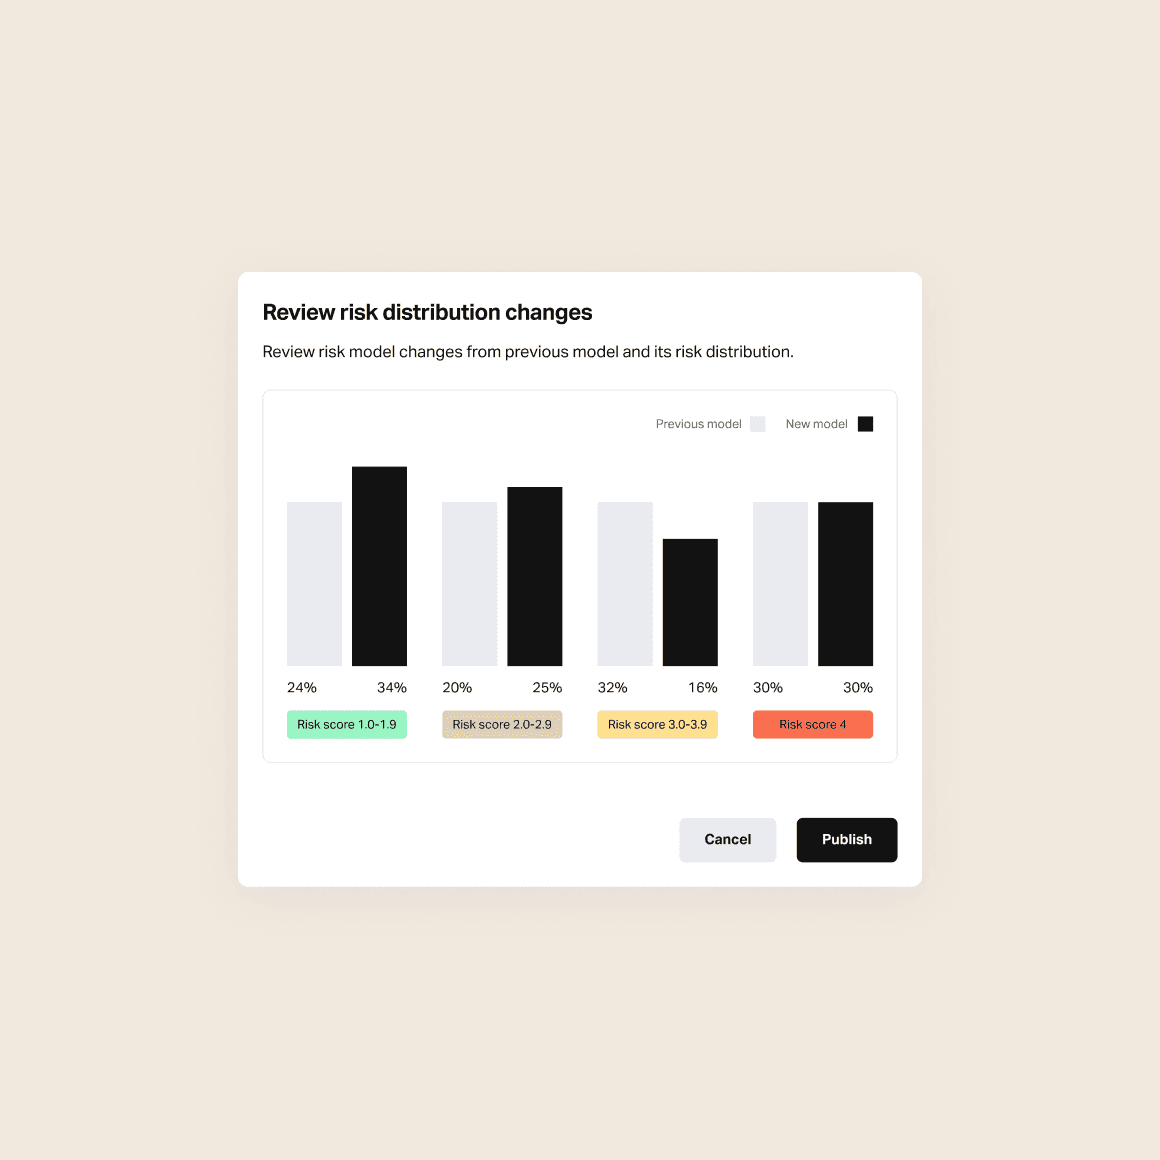
Define your methodology as variables and weights, preview its impact and publish it with a full version history.
Transaction monitoring
Monitoring tied to the customer
AMLR expects each transaction to be weighed against what you know about the customer. Bits rules read the risk profile directly.

Ongoing due-diligence
Due diligence that keeps itself current
Monitor customers daily across 1,300+ lists and refresh their data on the intervals your policy sets.
Case management
Decisions you can defend
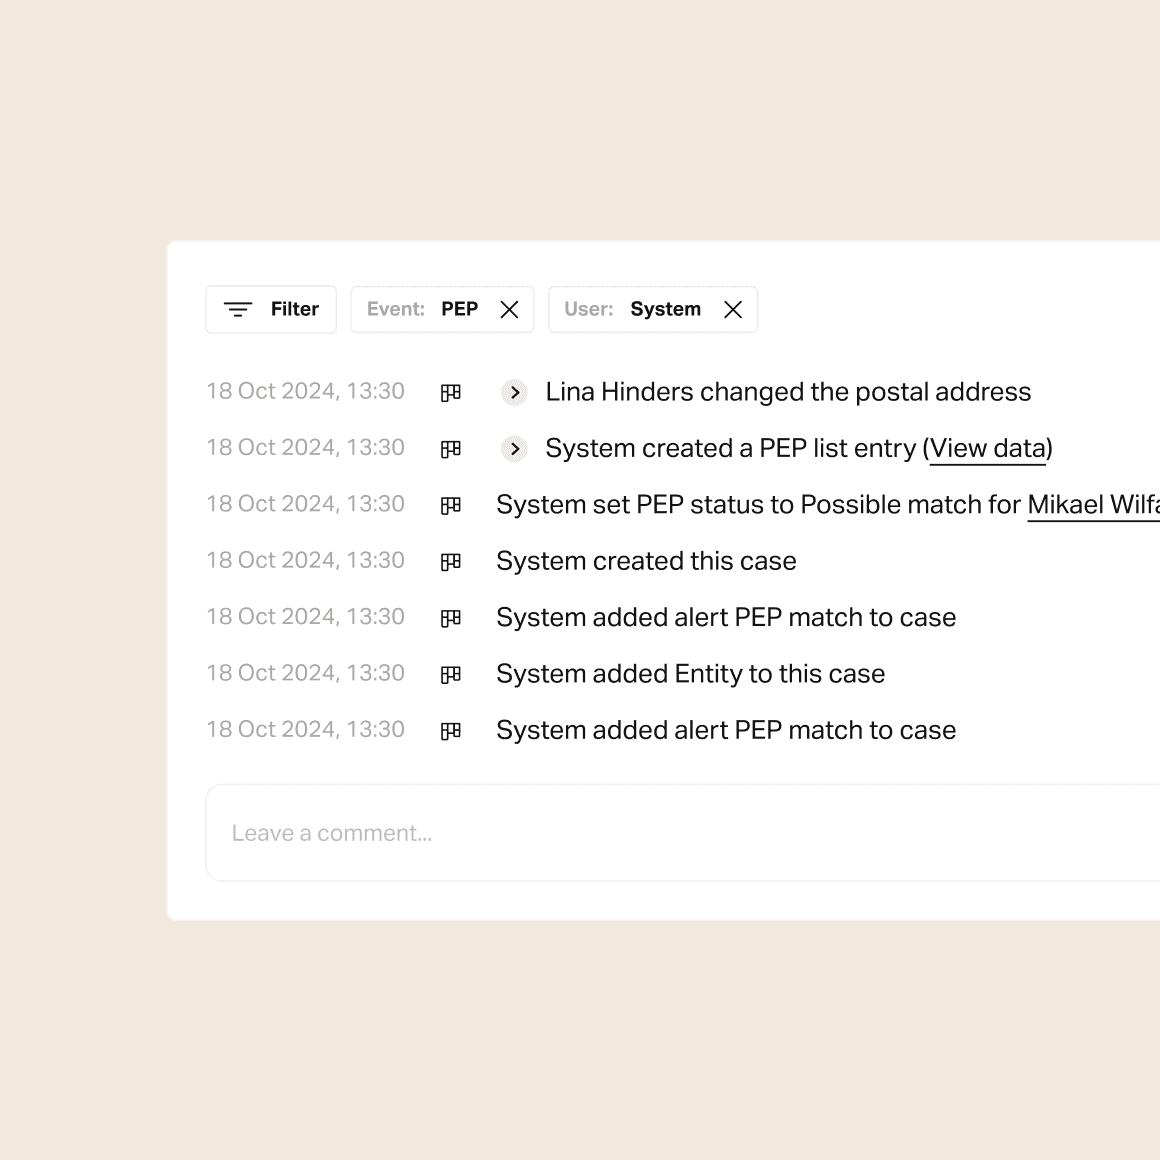
Each case keeps the customer record, triggered rules, comments and decisions in one timeline, ready for an auditor or your FIU.
Maja Chainska
Head of AML & Compliance Operations, Brite
Every solution runs on the same modules and the same customer record, so you can start with one and add the rest when you need them.
KYB & KYC onboarding
Onboard customers faster with custom workflows and automated checks across all your markets.
Explore →
AML risk score
A configurable risk model with custom variables, weights and a live score for every customer.
Explore →
Transaction monitoring
Rules that know the customer, fewer false positives and a full audit trail.
Explore →
Ongoing due-diligence
Daily monitoring across 1,300+ lists with granular rules and review intervals.
Explore →
Case management
Every case in one place, with collaboration, audit trail and PEP and sanctions data built in.
Explore →
Bits AI
AI agents that sort and summarize the work that used to take hours.
Explore →
You own the configuration. Your compliance team builds and maintains the rules in a no-code builder. No vendor requests or engineering tickets needed.
Audit-ready by default. Every configuration and event is recorded, so you can show an auditor what changed and when.
STR reports pre-filled. When you report a suspicion to your FIU, the system pre-fills the key data points, saving your team hours of manual work.
Connects to your tools. Bits connects to your transaction system and databases over webhooks and APIs.
When does AMLR apply?
What changes compared to today’s rules?
Do we need to replace our current tools?
How do we keep up as guidance develops?
Where can I learn more about AMLR?
Get started today.